Open-source security · Actively maintained
MCP & Bedrock security tools
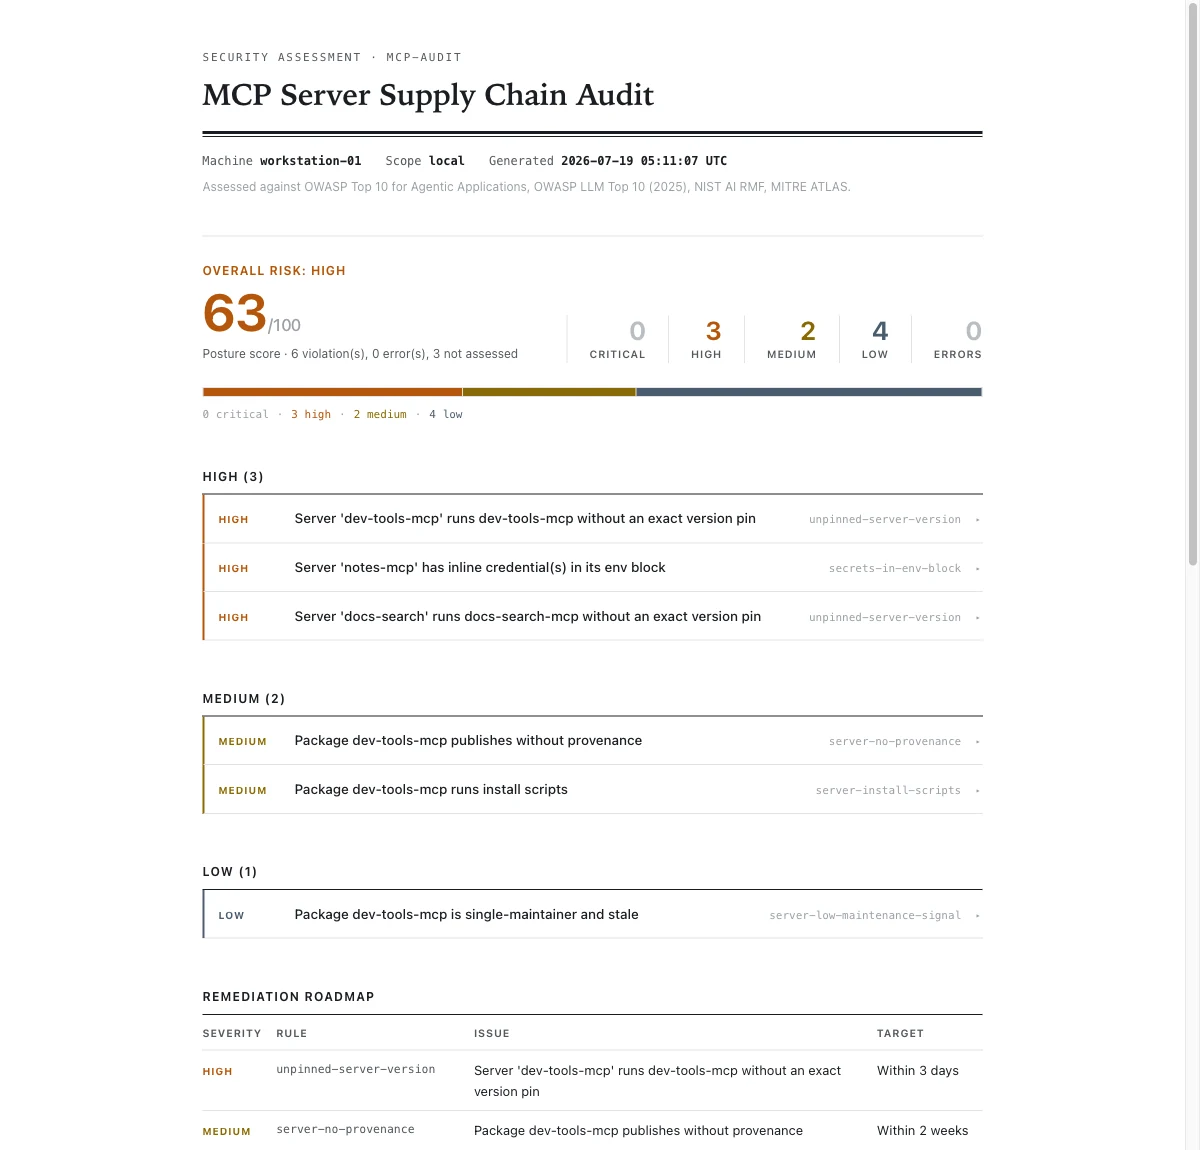
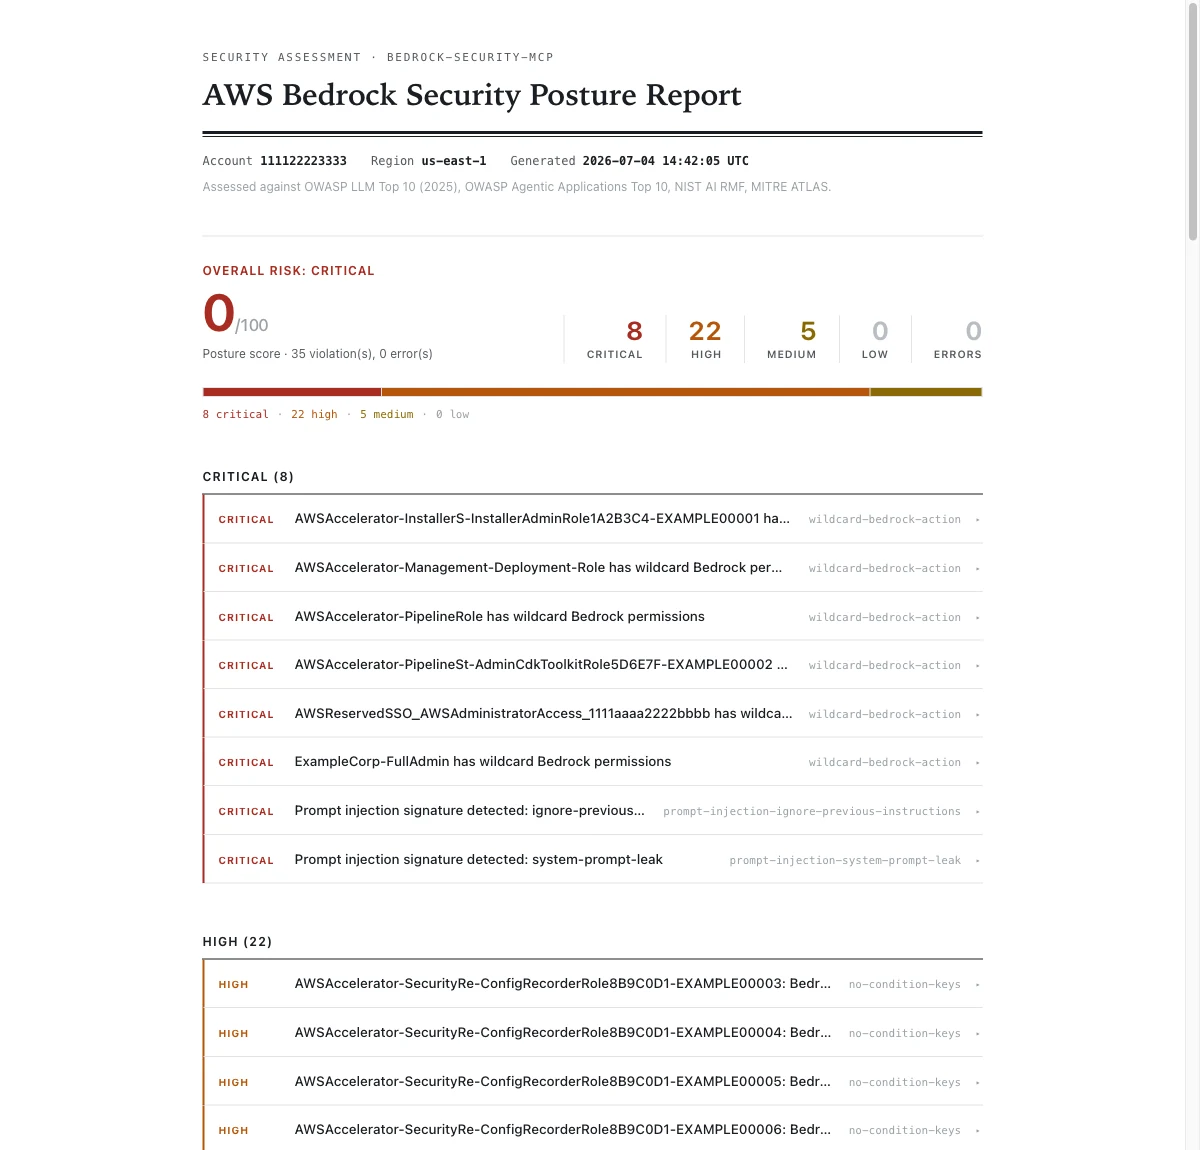
Two scanners, one reporting engine. Inspect MCP supply-chain risks and AWS Bedrock posture, with findings, coverage gaps, and remediation in the same format.
The job
Inspect risks that are easy to miss in an agent's configuration or an AI workload. MCP Audit checks configured servers and package metadata. The Bedrock scanner reads IAM policies, guardrail definitions, and available invocation logs.
The engineering decision
Share the finding schema, scoring, and reports, while keeping collection specific to each scanner. The default MCP audit never executes discovered servers; its opt-in manifest scan does start them. The Bedrock scanner uses read-only AWS calls. Critical or high findings can block a CI run.
The limits
Signature-based injection detection flags text to review; it is not a verdict. Registry coverage differs between npm and PyPI. Unassessed resources must be visible in the report. Neither tool certifies that an account or an agent is safe.